The handover happens at seven in the morning, in a stairwell, between two people who have never met. A cleaner waits for a building manager who is already late. The key is on a hook behind a desk, in a lockbox whose code has been texted to four people, or in the pocket of whoever opened last week. By the time the door is open, the building has lost ten minutes and gained a piece of unmanaged risk.
Recurring visitors sit in an awkward gap in most access policies. They are not staff, so they miss onboarding and offboarding. They are not guests, so nobody issues them a short-lived credential. They are cleaners, gardeners, pool technicians, electricians, lift contractors and seasonal crews, and the building depends on them arriving on schedule. This article is about structuring vendor access in property management so the handover disappears, without pretending the coordination problem has.
The three types of recurring visitor
Treating every recurring visitor as one group is the first mistake. Three patterns show up again and again, and each fails in a different way.
- Scheduled service. Cleaners, gardeners and pool technicians arrive on fixed days, often before staff. The same small team may serve the building for years. The risk is familiarity: access becomes permanent because nobody revisits it.
- On-call trades. Electricians, plumbers and lift engineers arrive when something breaks, often outside office hours, and the technician changes from visit to visit. The risk is speed: someone shares a code to avoid delaying a repair.
- Seasonal contractors. Window cleaners, painters and landscape crews appear in short bursts with larger teams and high turnover. The risk is volume: a key run or a shared code spreads faster than the record of who holds it.
Each pattern needs a different issue window and a different revocation rhythm. A single contractor-key policy will be too loose for one group and too slow for another.
Why keys fail for this group
Keys are durable, cheap and universally understood, which is why they survive long after the access policy around them has stopped working. For recurring visitors, four failures repeat.
- Copies multiply without a record. A key cut for a cleaner becomes a key passed to a supervisor, then to a replacement, and no list follows it.
- Handovers need two people present. The key has to move from someone who is leaving to someone who is arriving, which turns every visit into a small scheduling event.
- The record is physical and incomplete. A key tagged with a company name does not tell you which person used it, when, or whether the contract is still active.
- Loss has no clean endpoint. Without a per-person record, a missing key leads either to an unnecessary lock change or to no change at all.
The daily cost is coordination, but the strategic cost is visibility. A staff badge is tied to a payroll record. A contractor key is tied to nothing, so the building cannot answer the simplest question a project owner will eventually ask: who can still get in?
Temporary credentials as the design answer
An individual, time-bound credential removes the handover. The cleaner does not collect a key; the electrician does not borrow one; the seasonal crew does not share one. Each person is issued something that belongs to them and can be withdrawn from them.
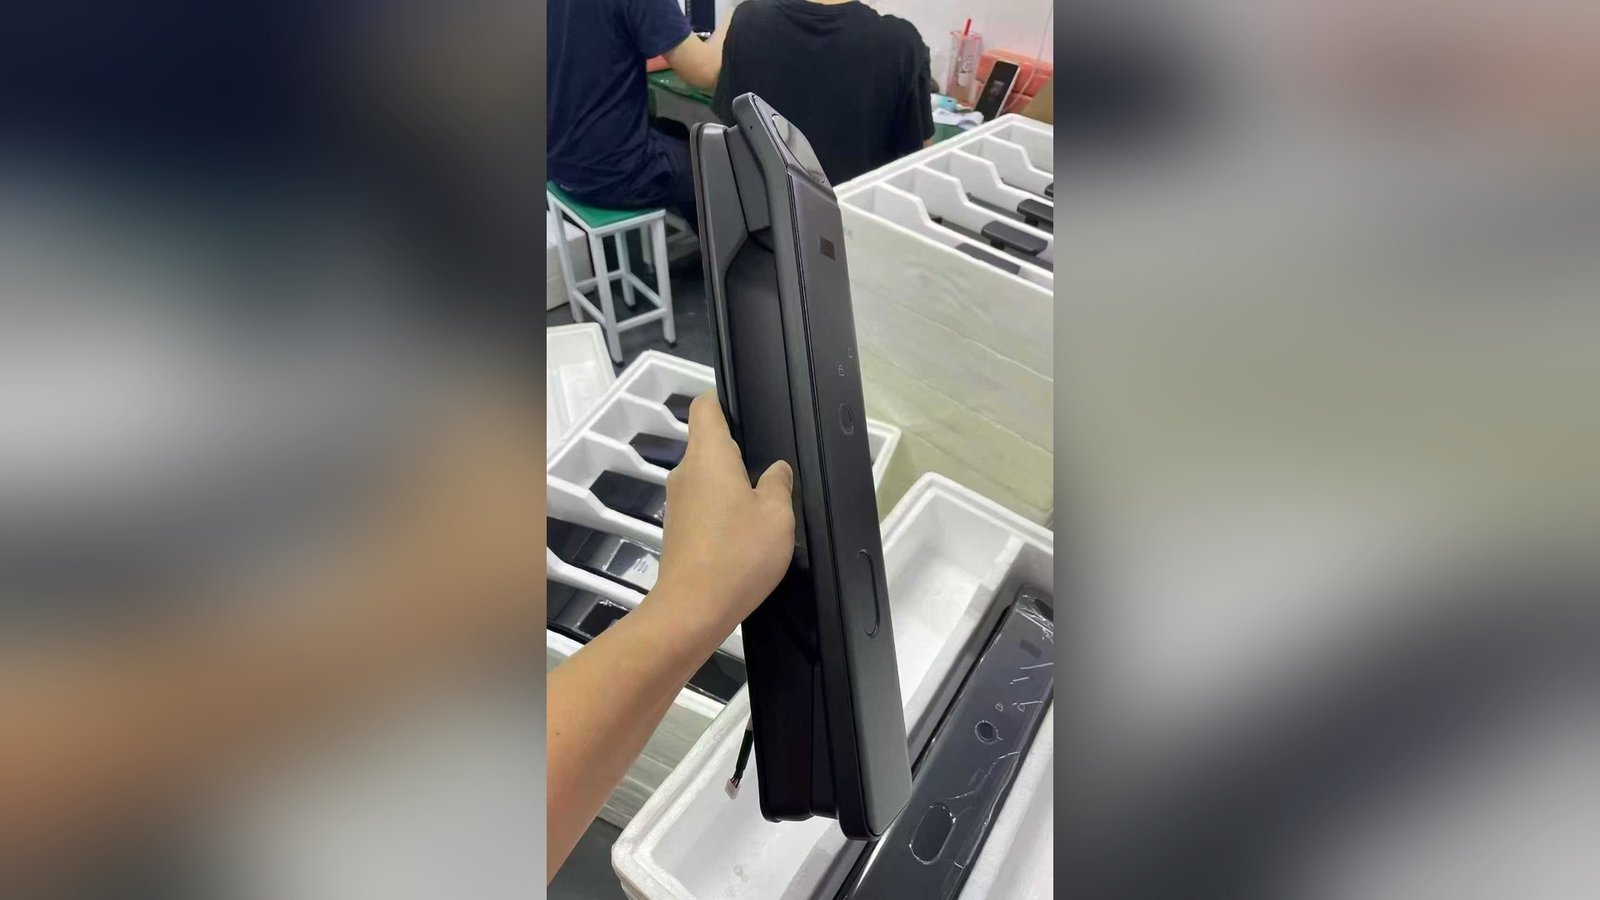
Capacity is documented per model. The DDZ17 room-door model is documented to support 300 users and temporary passwords. The DS-series deadbolts are documented at 100 fingerprints, 100 passwords and 100 cards. The DDL1 is documented for up to 297 user records with three admin positions. Those figures are for sizing, not targets. A building with forty recurring visitors does not need to fill a capacity; it needs enough headroom for turnover and a register that stays accurate.
Credential type should follow the person and the door. A card suits someone who already carries a site badge; a code suits someone who arrives without one; a fingerprint may suit a long-serving individual where the model documents it. The decision belongs to the operator, and so does the record. A lock can hold a credential. It cannot decide whether the person holding it should still have one.
Temporary is a process commitment. A credential is only temporary if the register names the end date and the person who will revoke it. Otherwise it is a permanent credential with an optimistic label.
Who owns revocation
Every access arrangement has an owner, whether or not the org chart says so. Name a primary and a backup, and give them the authority to say no. The owner issues, reviews and revokes; the backup covers holidays and sick days.
Revocation triggers should be written down before the first credential is issued: the last scheduled visit, the end of a contract, a lost card or exposed code, a duplicate discovered in the register, or a change of supervisor at the vendor. Ask the vendor to confirm departures rather than waiting to notice them. The discipline is close to staff offboarding and access revocation, with one difference: a vendor has no HR record in your building, so the contract has to carry the notification duty.
A periodic review closes the loop. An annual access audit is a reasonable baseline for stable sites; higher-turnover buildings may need it quarterly. The review is not a technical exercise. It is a comparison between the register and the people who are actually expected at the door next month.
Building the vendor register
The register can be a spreadsheet, a shared table or a page in the site file. What matters is that one version exists and someone owns it. At minimum, it should hold:
What each vendor record needs
- Vendor and the named person, not just the company.
- Door or doors, with enough location detail for a new staff member to find them.
- Access window: days, hours and any blackout periods.
- Credential type and an internal reference, never the credential value itself.
- Issue date and the person who issued it.
- Review or renewal date.
- Revocation owner and backup.
- Last confirmed visit and the next scheduled one.
- Escalation contact for a failed entry.
Keep the register clean. Duplicate entries are the usual failure: the same person issued twice under a slightly different name, or a credential left active after a replacement started. A short duplicate-credential check before each renewal catches most of it.
None of this requires a new department. It requires one named owner, a fixed review date and the refusal to issue a credential without an end point. The seven o’clock handover disappears because there is nothing left to hand over.
Planning access for a building full of recurring visitors?
CaremLock supplies room-door and deadbolt models for distributor and project orders, and documents user and credential capacities where those figures are verified. Send the door list and the visitor pattern, and our team will confirm what the documentation states for the models you are considering.
Or review the product range and contact the team.